

What it covers
Forensic investigation, breach legal advice, notifications to the Information Regulator and affected people, call-centre support, credit or identity monitoring where appropriate, and crisis communications.
When personal information is compromised, you have legal duties to act and a reputation to protect. This section funds the specialists who help you investigate, notify and communicate.
Forensic investigation, breach legal advice, notifications to the Information Regulator and affected people, call-centre support, credit or identity monitoring where appropriate, and crisis communications.

From the moment you discover or suspect a compromise of personal or confidential information, once you notify us through the incident hotline.
Where personal information lives, how it's protected (encryption, access control, logging), how long you keep it, and whether you could tell which records were affected.
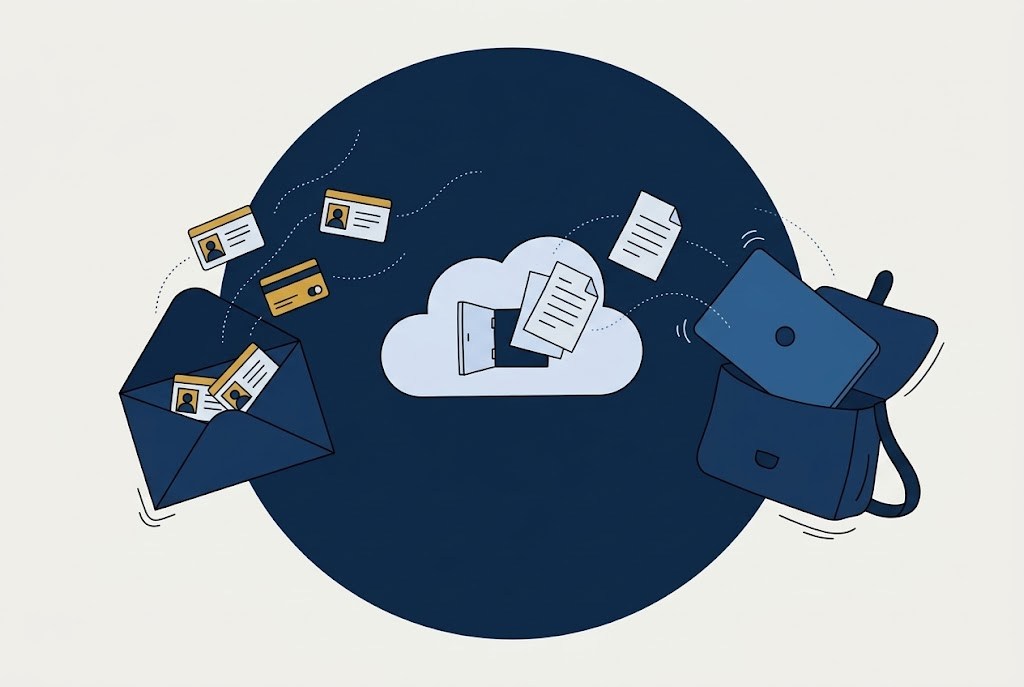
A staff mailbox containing years of client ID documents and bank details is accessed by an attacker for several weeks.
A misconfigured storage bucket leaves customer records publicly accessible until a researcher reports it.
An unencrypted laptop with HR records is stolen from a vehicle.
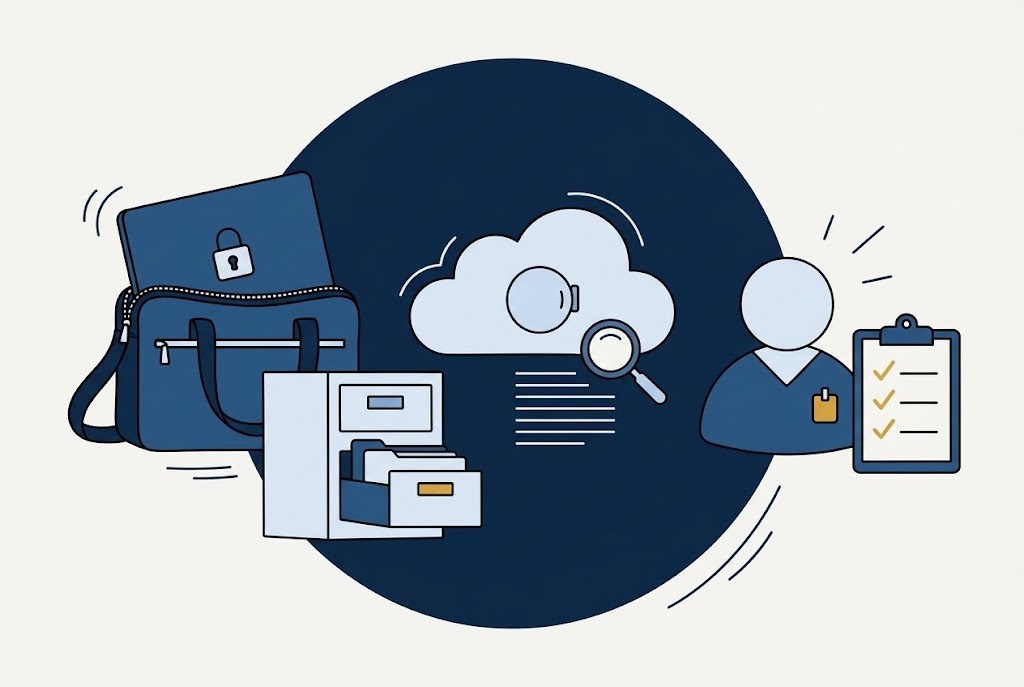
These are the controls that most influence our terms for this section of cover. Missing one doesn't automatically mean no cover. It means we'll talk about it, and explain the effect on your terms.
Section 22 of POPIA requires the responsible party to notify the Information Regulator and affected data subjects as soon as reasonably possible after discovering that personal information has been accessed or acquired by an unauthorised person. Breach counsel will advise on your specific obligations.
Start a Cyber Risk Check for a clear view of your exposure and what this cover could look like for you.
Get a Cyber Risk Check
Cover is subject to underwriting acceptance and to the terms, conditions, limits, sub-limits, deductibles and exclusions in the policy wording. [TODO: link to policy wording / product summary]